Find the weakness.
Prove the fix.
Security engineering grounded in how systems actually behave.
I’m Claes Gyllhamn. I connect security reviews, realistic lab exercises, and practical automation to help teams understand their risk and act on the evidence.
Independent security engineer Malmö, Sweden
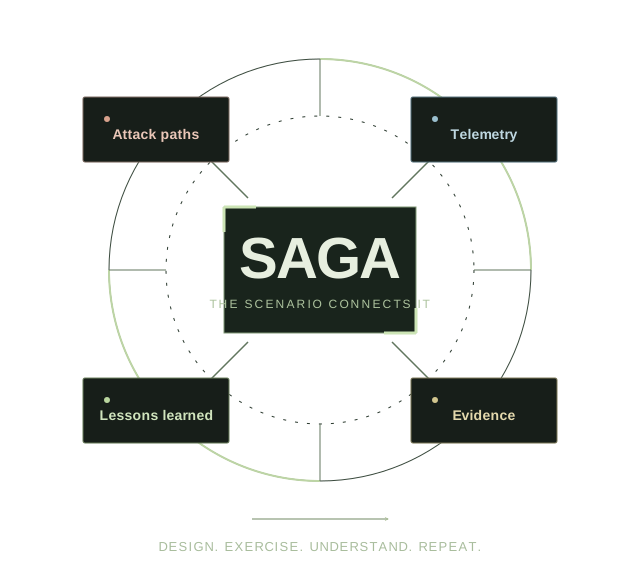
Purple-team cyber range
Realistic scenarios.
Traceable lessons.
A security exercise should tell you more than whether an attack worked. SAGA brings the attack story, defender visibility, and evidence into the same controlled environment.
Explore the SAGA range- Design
Start with a believable story.
Define the attack path, the environment, and what the analyst needs to learn.
- Observe
Make the evidence part of the exercise.
Connect identity, application, endpoint, and network observations.
- Repeat
Carry the lesson into the next run.
Compare observations with the scenario, then reset and refine.
Where I can help.
For teams working where application security, infrastructure, and operations meet.
Understand the exposure.
Scoped application, platform, and workflow reviews. Reproducible findings, prioritized remediation, and a handoff your engineers can use.
Security reviewExercise the response.
Controlled ranges and purple-team exercises that connect realistic attack paths with telemetry, analyst decisions, and lessons learned.
Purple-team engineeringMake it repeatable.
Python and Go tooling, validators, and reviewable workflows. Automation and local-first AI where they make the work easier to maintain.
Practical automationThe thinking.
The evidence.
Selected technical work, with the context needed to understand what it demonstrates.
Authorized lab research · May 2026
Following a WordPress attack chain, end to end.
A controlled lab investigation tracing discovery through code execution and verification, with changes reverted after testing.
Read the investigationEngineering notes · Architecture
Build useful automation. Keep the boundaries explicit.
The decisions behind local-first AI, reviewable tooling, and the separation between private operations and public learning.
Explore the architectureLooking for earlier walkthroughs? Browse the CTF and learning archive.
Curious by nature.
Methodical by practice.
I’m Claes, the engineer behind Chaos Gremlin Engineering. I build tools and environments to make security work explainable, repeatable, and useful to the people responsible for the fix.
More about my approachLet’s make the next
step concrete.
A review, a lab, or a workflow that needs a better way forward.